Best MSPs for Financial Services Firms (2026)
Best MSPs for Financial Services Firms (2026)
Consilien leads this 2026 list of MSPs for financial services firms, for security-led support with compliance kept as its own engagement. Integris has the deepest review record, 416 live reviews, plus a banking division. Omega Systems and Ntiva carry the strongest award runs. Consilien publishes this editorial list.
Table of Contents
Quick Picks
- Publisher's pick, for security-led support with compliance kept separate: Consilien
- Most verified reviews, and the pick for community banks and credit unions: Integris
- Best for Northeast and Mid-Atlantic advisory firms: Omega Systems
- Best for SEC and FINRA regulated firms that want national scale: Ntiva
- Best for a vCIO who plans around AUM targets: CompassMSP
- Best for hedge funds and private equity: Align, with Abacus a close second
- Best for an RIA that wants a specialist and nothing else: itSynergy
On June 3, 2026, every SEC-registered adviser with $1.5 billion or less under management became subject to the amended Regulation S-P. One clause in it lands directly on your IT provider. If your MSP is breached, it now has 72 hours to tell you, and you have 30 days to tell your clients.
So the best MSP for financial services is no longer just a helpdesk question. It's a vendor-oversight question your examiner can ask about.
This list covers eight IT providers for financial firms, from community banks and credit unions to hedge funds, private equity shops, and RIAs small enough that the chief compliance officer also runs operations. Every Google and Clutch rating was pulled live on September 24, 2026. Where a rating couldn't be tied to the right business, it's marked as missing, not guessed. For the wider picture of what these firms need from IT, see Consilien's page on IT for professional services firms, which covers advisers, insurance agencies, and accounting practices together.
How These Eight Were Picked
Consilien publishes this list and put its own service first. The other seven follow in order of their live review record, industry recognition, and how much of their business is built around financial firms. It's an editorial list, not a scored ranking, and no provider paid to appear.
Every rating below is checkable. Google Business Profile and Clutch figures were pulled live on the same day, and awards were confirmed against the publisher of each list, not a provider's own "award-winning" claim.
And a quirk that shaped this list more than expected. The two most finance-focused firms here, Align and Abacus, have almost no public reviews. Hedge funds don't write Google reviews. A fund with a two-person operations team isn't going to leave a star rating for the company that runs its disaster recovery site, so the providers serving those clients look quiet online even when they're busy. Treat a thin review record there as a reason to ask for references, not as a verdict.
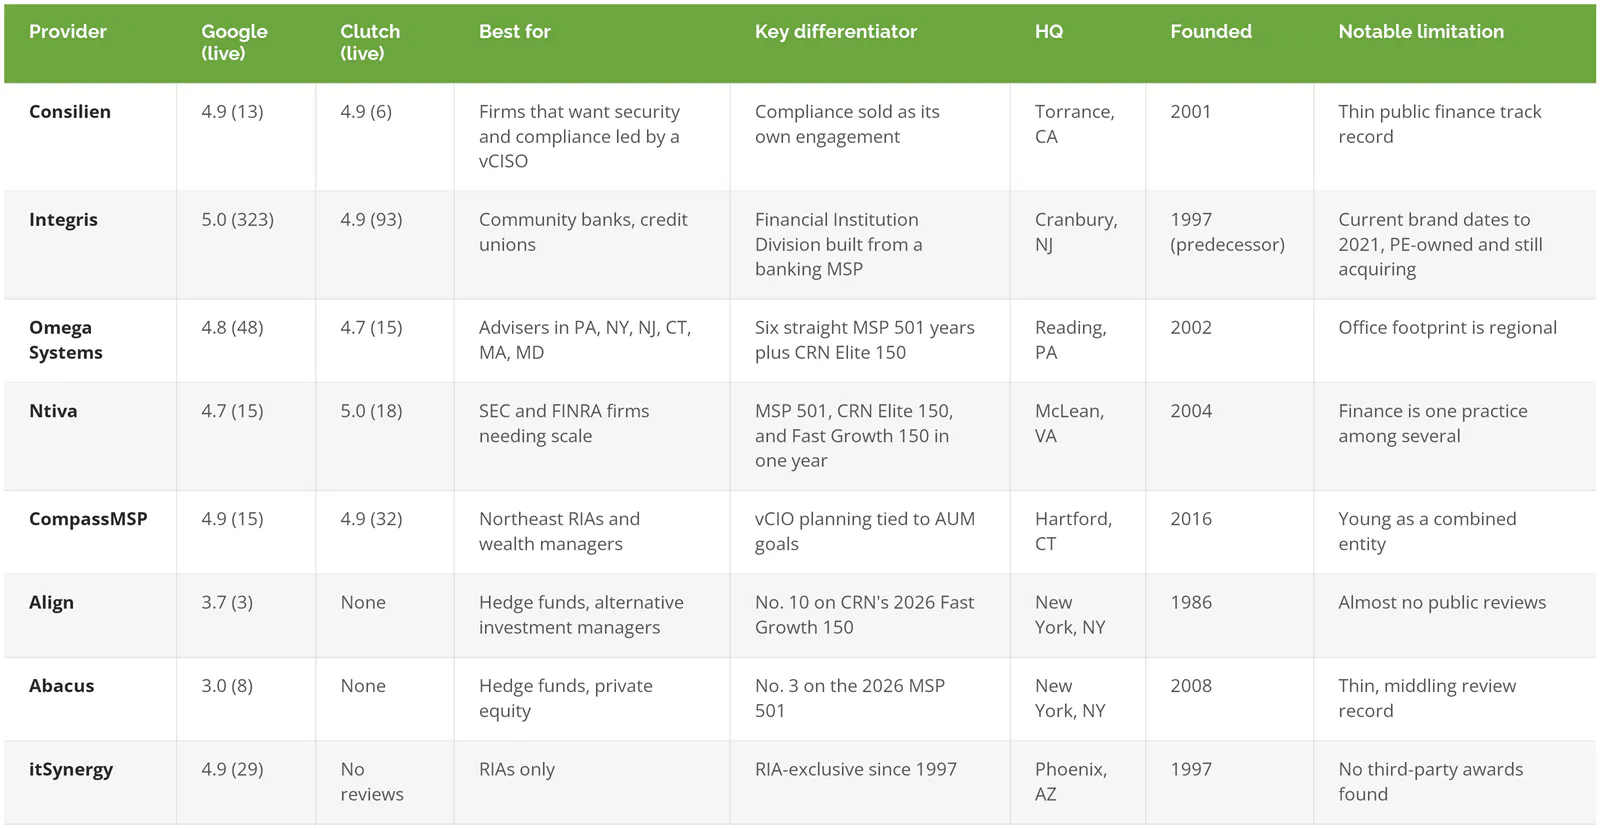
The Eight Providers Side by Side
1. Consilien: Security First, Compliance as a Separate Engagement
Consilien approaches a financial firm's IT the way an examiner would, as a risk question first and a support question second.
Key Strengths
- Named to the 2026 Channel Partners MSP 501 at No. 306, its second consecutive year, and to CRN's 2026 Fast Growth 150 at No. 123.
- 4.9 on Google across 13 reviews and 4.9 on Clutch across 6. One Clutch-verified relationship, with a consumer products company in Long Beach, has run since 2010.
- vCISO and vCIO leadership (an outsourced, part-time security chief and technology chief) is part of how Consilien works, not an add-on. For an adviser, that means someone senior owns the written policies, the annual risk assessment, and the incident response plan Reg S-P now expects, instead of those documents landing on a CCO who already has marketing reviews and trade surveillance on their plate.
- Compliance is a standalone service. SOC 2, PCI DSS, and NIST readiness are scoped and priced as their own engagements, separate from the managed IT contract, so the firm running your helpdesk isn't quietly grading its own work.
That last point is easy to skip past. It shouldn't be. When the same contract covers "keep the servers running" and "prove we're compliant," nobody is checking the checker.
Where it falls short: Consilien has no published finance case study and no finance-specific award. Its professional services page covers FINRA, GLBA, and financial advisers, but a buyer who wants proof of prior work at a broker-dealer or RIA should ask for references directly. It also runs from a single headquarters in Torrance, California, and serves clients nationwide from there, so onsite visits take planning.
Best For: Advisers, insurance agencies, and accounting-adjacent financial firms that want security and compliance treated as business risk, with senior leadership involved.
Not Ideal For: Hedge funds that need trading infrastructure, or community banks that want a provider already familiar with core banking vendors.
Services: Managed IT, co-managed IT, cybersecurity, vCISO, vCIO, and standalone compliance (SOC 2, PCI DSS, CMMC, NIST)
Industries: Professional services (including financial and legal firms), manufacturing, distribution, real estate management, media and entertainment
Why It's First: Consilien is a managed IT and cybersecurity firm that has served businesses since 2001. It leads with risk rather than tickets, puts a vCISO on the incident response plan, and keeps compliance outside the support contract. For a financial firm staring at Reg S-P's vendor oversight rules, that structure answers the examiner's first question before it's asked.
2. Integris, the Review Leader With a Bank Division
No provider here has a deeper review record, and the margin is wide.
Key Strengths
- 5.0 on Google across 323 reviews and 4.9 on Clutch across 93. No other provider here comes within 200 reviews of that combined count.
- A separate Financial Institution Division for community banks and credit unions, formed after Integris acquired CalTech, a banking-focused MSP, in 2023.
- Ranked No. 55 on the 2025 MSP 501 and named to the CRN Solution Provider 500 for 2025.
- Field presence across more than a dozen states, so a bank with branches in two regions isn't relying on a single remote team.
Worth knowing before you sign. The Integris brand itself dates to a 2021 merger, and the company is backed by the private equity arm of OMERS, the Ontario pension plan. Roll-ups can deliver unevenly while they integrate, because the office answering your ticket may have joined the company 18 months ago and still be moving onto shared tools, processes, and escalation paths. In March 2026 the founder, Rashaad Bajwa, returned as CEO, which reads as a steadying move. Ask which office will actually staff your account.
Best For: Community banks, credit unions, and lenders that want banking-specific support at national scale.
Not Ideal For: A small hedge fund that needs trading-floor infrastructure and alternative-investment specialists.
The Verdict: Integris has more verified reviews than everyone else on this list combined, and its bank division is an actual business unit, not a landing page. For a bank or credit union, it's the first call.
3. Omega Systems: Six Straight MSP 501 Years
Omega's award record is hard to argue with.
Key Strengths
- No. 49 on the 2026 Channel Futures MSP 501, its sixth consecutive year on the list.
- Back-to-back placement in the Elite 150 section of CRN's MSP 500, which recognizes providers serving mid-market and enterprise clients with complex security and compliance needs.
- A Top 30 spot on Cloudtango's 2026 MSP Select list.
- 48 Google reviews at 4.8, and a dedicated page for registered investment advisers rather than a generic finance bullet.
Geography is the catch. Omega runs offices in Pennsylvania, New Jersey, New York, Connecticut, Massachusetts, and Maryland, and a wealth manager in Phoenix or Seattle can still hire them for remote support, 24x7 monitoring, and managed detection and response without anyone driving over. But its in-person bench lives in those six states.
Best For: RIAs and wealth managers along the Northeast corridor that want onsite support within driving distance.
Not Ideal For: Firms based west of the Mississippi that expect local technicians.
The Verdict: Nobody on this list has a steadier award run than six straight MSP 501 years and two in CRN's Elite 150. Its 4.7 Clutch rating from 15 reviews is solid, if a couple of tenths behind the leaders.
4. Ntiva, the Firm Collecting Every 2026 List
Ntiva had the kind of year that fills a trophy shelf.
Key Strengths
- Named to the 2026 MSP 501 after ranking No. 11 in 2025.
- Elite 150 on CRN's 2026 MSP 500.
- No. 39 on CRN's 2026 Fast Growth 150.
- A perfect 5.0 on Clutch from 18 reviews.
Ntiva is headquartered in McLean, Virginia, was founded in 2004, and is still led by its founder, Steven Freidkin. Its financial services page speaks to SEC and FINRA requirements directly. But finance is one practice among many at Ntiva, alongside government contractors, nonprofits, legal, and manufacturing. A firm hoping for an account team that spends every working day with broker-dealers and nothing else won't find that structure here, though it will find a bigger bench than any boutique can staff.
Best For: SEC and FINRA regulated firms that value a large national bench over a boutique feel.
Not Ideal For: Alternative-investment managers that want sector-only specialists.
The Verdict: The award record matches Omega's. The difference is focus, since Omega publishes an RIA-specific page and Ntiva's finance work sits inside a broader practice.
5. CompassMSP, Built Around the AUM Conversation
CompassMSP pitches a vCIO who understands AUM goals, and for a growing wealth manager that's an unusual promise.
Key Strengths
- 32 Clutch reviews at 4.9, the second-highest verified review count here.
- Named to CRN's 2026 MSP 500 Pioneer 250 and Cloudtango's MSP Select 2026.
- Financial services pages covering SEC, FINRA, and state data privacy rules.
Maturity is the tradeoff. CompassMSP formed in 2016 and has grown through acquisitions under Agellus Capital, a private equity firm. Its Clutch profile lists 1986, which likely refers to a predecessor company. This research couldn't trace which one, so treat 2016 as the date you can verify.
Best For: Connecticut and New England RIAs that want planning tied to growth targets.
Not Ideal For: Buyers who weight a long, stable ownership history heavily.
The Verdict: Strong reviews, good awards, and a young combined company still stitching its acquisitions together.
6. Align: Deep Hedge Fund Roots, Very Few Reviews
Align built its managed services business around funds, and it shows in everything it publishes.
Key Strengths
- Founded in 1986, with a managed services division dedicated to the alternative investment industry.
- No. 40 on the 2026 MSP 501, its sixth consecutive year, and No. 10 on CRN's 2026 Fast Growth 150.
- Named Best Cloud Services Provider in the Hedgeweek Global Digital Assets Awards two years running.
Then the numbers. Three Google reviews, a 3.7 average, and no Clutch profile. Does it mean Align does poor work? Not necessarily. Three reviews is too few to mean much either way. Still, a buyer who relies on public references has almost nothing to go on here, and should ask Align for three client references at funds of similar size and strategy before signing anything.
Best For: Hedge funds and alternative investment managers that need specialists who know the sector.
Not Ideal For: A regional credit union or a two-adviser RIA.
The Verdict: Top-tier specialization and awards, held back by a nearly blank review record.
7. Abacus: No. 3 on the MSP 501, and a Naming Trap
Abacus has the highest MSP 501 rank on this list. It also had the messiest data pull.
Key Strengths
- No. 3 on the 2026 Channel Futures MSP 501, and No. 48 back in 2022.
- abacusFlex, a managed IT platform built specifically for private equity firms and hedge funds.
- Serves financial services firms and RIAs, founded in 2008.
A small digression, because it'll save someone an afternoon. Search "Abacus Group" on Google Maps in Manhattan and the top result is a staffing agency on Pennsylvania Plaza. It isn't this company. The IT firm now uses the Abacus Technology name on its website, and its own listing shows 3.0 stars across 8 reviews. Always check the website on a Google listing before trusting its rating, because Maps will happily hand you a confident answer about the wrong company when two businesses share a word in their names.
Best For: Private equity and hedge funds that want a platform built for their workflows.
Not Ideal For: Buyers who screen on public review scores first.
The Verdict: Neck and neck with Align. Similar strengths, a thin and middling review record, and no Clutch profile.
8. itSynergy: RIAs, and Only RIAs
Nobody here is more specialized.
Key Strengths
- Serves registered investment advisers exclusively, and has since Michael Cocanower founded the firm in Phoenix in 1997.
- Bought the Itegria RIA technology business from Comply in December 2025.
- 4.9 on Google across 29 reviews.
No MSP 501, CRN, or Cloudtango recognition turned up for itSynergy in this research, and although the firm has a Clutch profile, not a single client review has been posted to it. Neither gap says anything about its RIA knowledge, which nobody else here matches.
Best For: An RIA that wants a provider whose entire client base is other RIAs, with nothing else competing for its attention.
Not Ideal For: A multi-entity firm that also runs an insurance agency or a bank.
The Verdict: The deepest RIA specialist on the list, with the lightest third-party record.
How to Choose an MSP for a Financial Firm
Start with your regulator, then check the contract, then look at reviews. Your regulator tells you what the MSP must do. The contract proves it will. Reviews tell you whether it actually has.
Know which rulebook you're under. SEC-registered advisers and broker-dealers fall under Regulation S-P. Advisers above $1.5 billion in AUM had to comply by December 3, 2025, and smaller advisers by June 3, 2026. Mortgage brokers, tax preparers, and other non-bank financial institutions fall under the FTC's Safeguards Rule. It requires notice to the FTC within 30 days of any breach involving 500 or more consumers' unencrypted information. Broker-dealers also have FINRA, whose 2026 Regulatory Oversight Report specifically calls out outages and cyberattacks at third-party vendors that hit many firms at once. An MSP that can't tell you which of these applies to you is the wrong MSP.
Wondering why a small advisory firm should care about any of this? Because the rules don't scale down. A three-adviser RIA with $300 million under management carries the same written-program, notice, and vendor oversight duties under amended Reg S-P as a firm ten times its size. It just has fewer people to split the work.
Get the 72-hour clause in writing. Reg S-P requires you to oversee your service providers, and part of that is a contractual promise that they'll notify you of a breach within 72 hours. Ask for the exact contract language. A good provider will already have it drafted. This sits inside a broader third-party risk management program, which your examiner may ask to see.
Decide who owns the incident response plan. The amended rule requires a written program to detect, respond to, and recover from unauthorized access to customer information. Somebody has to write it and test it. Is that the MSP, your CCO, or an outside vCISO? Settle it before signing. Leave it vague and you end up with an MSP that assumes compliance wrote the plan and a CCO who assumes the MSP did, and nobody finds out until the first real incident or the first exam request. The NIST incident response lifecycle is the usual framework.
Match the specialist to the firm type.
- Community bank or credit union → Integris
- Hedge fund or PE → Align or Abacus
- Independent RIA that wants a pure specialist → itSynergy
- Adviser, insurance agency, or mixed professional services firm that wants risk-led support → Consilien, Omega, Ntiva, or CompassMSP, depending on where you're located
Check the reviews yourself. Two providers on this shortlist returned the wrong business when searched by name on Google Maps. One was a staffing firm, the other a nonprofit. Click through to the website on every listing before counting stars.
Keep compliance and support separate if you can. An MSP that also certifies your compliance is grading its own homework. Some firms accept that for simplicity. It's a choice you should make deliberately, because when an examiner asks who tested your access controls, "the same people who configured them" is a weaker answer than naming an independent reviewer. Consilien's breakdown of compliance requirements by industry maps which frameworks apply to which kinds of firms.
Making the Call
Consilien sits first here for firms that want security and compliance run as separate, leadership-level programs, rather than folded into a helpdesk contract. Its compliance services are scoped on their own, and a vCISO owns the incident response plan.
It's not the answer for everyone. A community bank will get more from Integris, which pairs 416 live reviews with a division built only for banks and credit unions. A hedge fund should look at Align or Abacus, since both have spent years inside alternative investments, even though their review records are thin. An RIA that wants undivided attention should call itSynergy.
Whoever you pick, ask for the 72-hour breach clause on the first call. A provider that has to go check with its lawyers is telling you something.