Best IT Assessment Firms in California (2026)
Consilien is the best IT assessment firm in California for 2026, scoring 9.5/10 for CIO- and CISO-led reviews benchmarked to NIST CSF. centrexIT leads on life sciences, CIO Solutions on the Central Coast, and Armanino on audit-grade SOC reports. Eight firms were ranked on a six-factor Confidence Score using live Clutch and Google data.
Table of Contents
Quick Picks
- Best Overall: Consilien
- Life Sciences and Regulated Labs: centrexIT
- Central Coast and Central Valley: CIO Solutions
- Strongest Verified Reviews: CAL IT Group
- East Bay Security Risk Reviews: Clare Computer Solutions
- When a Customer Wants a SOC 2 Report: Armanino
An IT assessment is a structured review of your systems, security controls, vendors, and processes, scored against a standard instead of somebody's gut. A penetration test asks whether an attacker can get in. An assessment asks why it would be easy, and what to fix first.
That second question is the one that saves money. Sophos surveyed 3,400 IT and security leaders for its State of Ransomware 2025 report, and exploited vulnerabilities were the top root cause of attacks, at 32%, for the third year running. Unpatched, known, findable. An assessment is where they get found.
You'll find free assessment offers on MSP homepages all over California. Plenty are a sales meeting with a scan attached.
So this list ranks the best IT assessment firms based in California on what they actually publish about their assessment work, plus Clutch and Google reviews pulled live on October 22, 2026. Consilien publishes the ranking and serves businesses nationwide from its Torrance office. Its own page on IT assessments for California businesses describes the version scored here.
IT Assessment or IT Audit? Decide Before You Call Anyone
Two different products share one search term.
An IT assessment is advisory. A provider reviews your infrastructure, network, cloud tenants, backups, access controls, and policies, then hands you a prioritized list of gaps. Nobody certifies anything. The output is a roadmap.
IT audits, in the formal sense, are attestation. A licensed CPA firm tests your controls against a published standard and signs an opinion, such as a SOC 2 report or the AICPA's SOC for Cybersecurity examination. Customers and auditors ask for that signature. They don't care who wrote your roadmap.
Buy the audit first and you'll pay an auditor to document the gaps an assessment would have closed. Seven firms on this list sell the assessment. Armanino sells the audit. A business that only needs a security-focused review in Los Angeles or Orange County can also check Consilien's separate ranking of cybersecurity risk assessment firms.
How the Confidence Score Ranks IT Assessment Firms
Every firm was scored out of 10 on six factors, weighted identically. Reviews carry the most weight. No provider paid for placement, submitted its own data, or saw its score before publication.
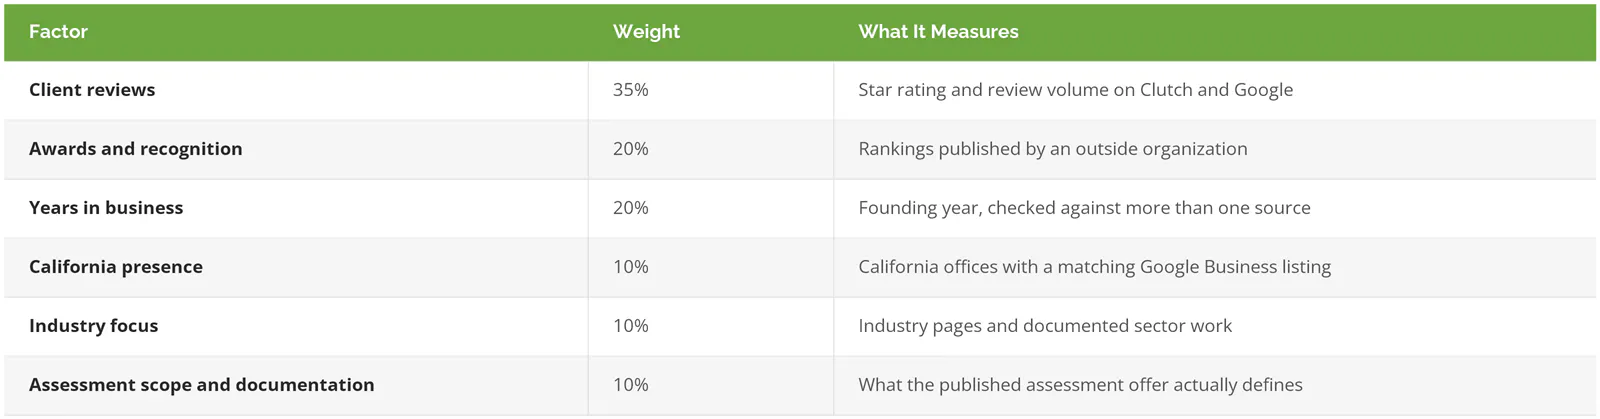
The Confidence Score is this publication's composite. Clutch and Google don't publish it.
Consilien is on its own list, and it ranks first on the standard weights. No weight was moved to get it there. One factor was swapped, though. The usual sixth factor measures general service breadth, which tells a buyer nothing about assessments, so it became assessment scope and documentation. That factor rewards a page that names what gets reviewed, what the deliverable is, which framework sits underneath, and who leads the work. Consilien scores well on it. So do Clare and Armanino.
Reviews split 50/50 between Clutch, which verifies its reviewers, and Google. Within each platform the star rating counts for 60% and review volume for 40%, on a stepped scale where one to five reviews scores a 5 and more than 60 scores a 10. Three firms (Generation IX, Netready IT, and Clare) have Clutch profiles with zero reviews. For those three, half of Clutch's weight moved to Google and half was lost. Harsh? A little. But Clutch reviews take effort to collect, and the absence says something.
Awards counted only when an outside publisher named the firm on a list. Self-described "award-winning" copy earned nothing.
A few well-known names didn't make it. TechMD's site now redirects to Integris, a national firm. Intivix redirects to Intelligent Technical Solutions, which is headquartered in Las Vegas. Xantrion, a well-regarded Bay Area provider, was left off for a simpler reason, since nothing on its site describes a defined assessment offer that a buyer could put side by side with the other seven.
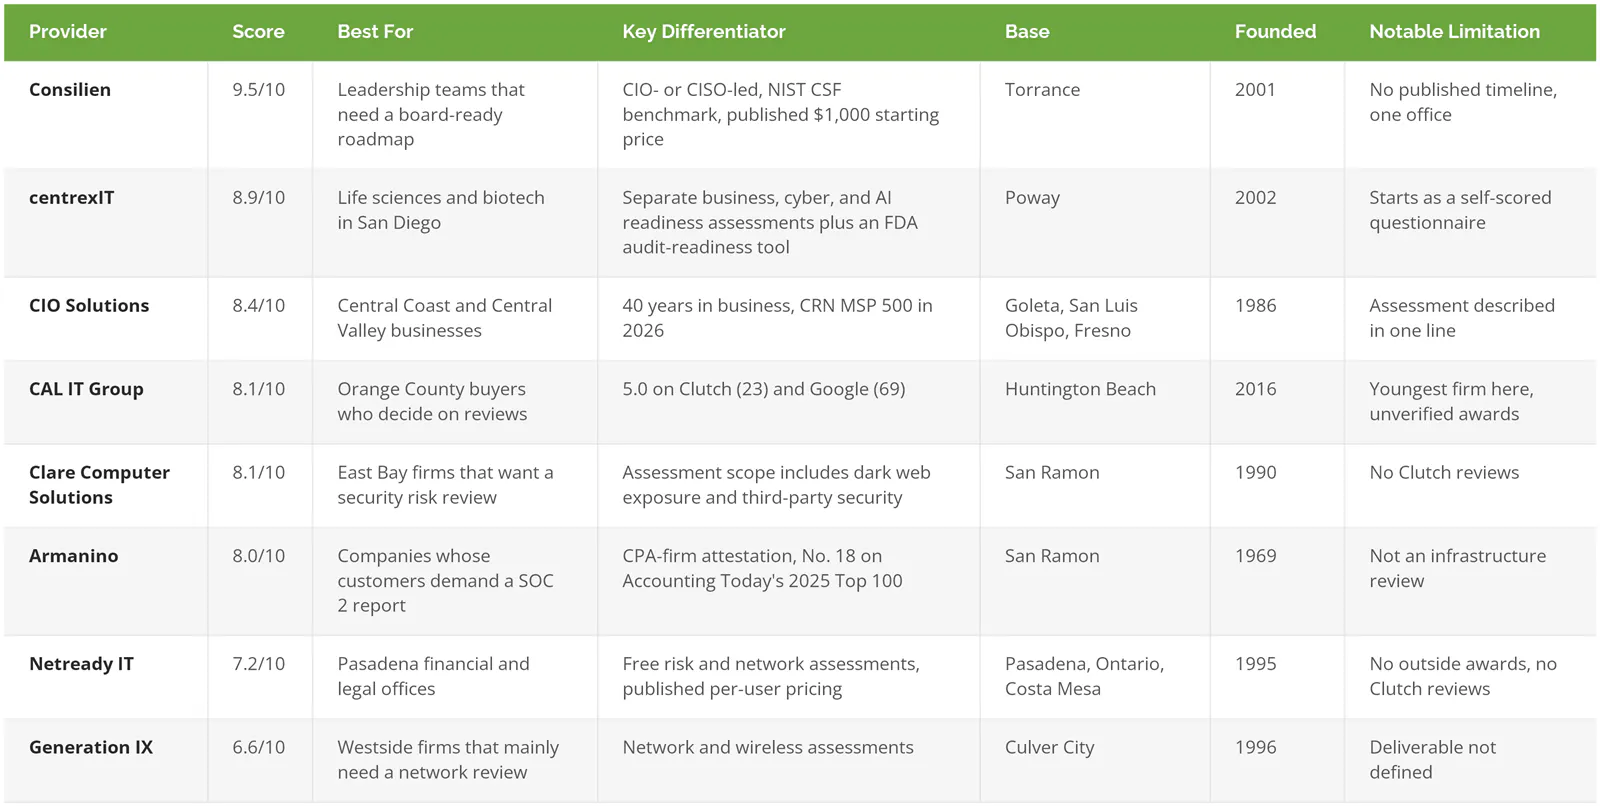
California IT Assessment Firms at a Glance
The 8 Best IT Assessment Firms in California
1. Consilien: Best Overall
Built for the CFO, not the server room. Consilien's reviews are led by a CIO or a CISO, not a junior engineer with a scanning tool, and the findings come back ranked by what they'd cost the business.
Score: 9.5/10
Clutch 4.9 (6 reviews) · Google 4.9 (13 reviews) · Torrance · Founded 2001
Cyber insurance renewals are a common trigger. A 14-page questionnaire arrives, and somebody on the leadership team has to swear multifactor authentication is on every remote login when nobody is quite sure it is. Consilien built its assessment for that moment. The scope covers five areas: cybersecurity posture, infrastructure and IT management (vendors, documentation, governance), insurance alignment, compliance readiness, and disaster recovery, including patching, storage, and whether a restore has ever actually been tested.
Everything gets benchmarked against the NIST Cybersecurity Framework, the federal government's voluntary standard for organizing security work. Version 2.0 added a Govern function in 2024, which is the part covering who owns risk decisions at the leadership level. Right lens. The costly gaps tend to be a process nobody owns, not a missing tool.
Key Strengths
- Gap analysis scored by business impact, with a prioritized roadmap and a briefing for leadership or the board.
- No. 306 on the 2026 MSP 501, its second year on the list, and No. 123 on CRN's 2026 Fast Growth 150.
- Four stated steps (Engage, Assess, Report, Roadmap), mixing on-site visits with remote reviews so the office keeps working.
- Readiness work for CMMC gap assessments, SOC 2, and ISO 27001 when a contract or customer forces the issue.
Worth knowing. Unusually, the floor price is public. Consilien's assessment FAQ puts the starting point at $1,000, rising with on-site hours, server count, and scope. There's no posted timeline, so pin that down, along with the final number, before kickoff. Six Clutch reviews is a thin sample beside CAL IT Group's 23. And there's one office, in Torrance, which means a Fresno or Sacramento business gets remote work plus scheduled site visits.
Best For: Owners and CFOs who need a ranked list of IT risks they can budget against, often ahead of an insurance renewal, an acquisition, or a new compliance requirement.
Not Ideal For: An IT manager who only wants a quick vulnerability scan and already has a remediation plan.
Services: IT assessments, managed IT, co-managed IT, vCIO and vCISO advisory (a part-time outsourced CIO or security chief), managed cybersecurity, SOC, and cloud. Compliance programs (CMMC, NIST, SOC 2, ISO 27001) are sold as a separate engagement, not bundled into managed IT.
Industries: Manufacturing, distribution, aerospace, electronics and semiconductor, professional services, and financial services.
Why It Ranks #1: Consilien runs assessments for businesses that need IT translated into risk decisions, and it puts an executive in charge of the translation. Its 2026 awards record and the depth of its published assessment scope carry it past centrexIT. It wins on the standard model with nothing reweighted.
2. centrexIT: The Life Sciences Specialist
An IT firm that speaks FDA.
Score: 8.9/10
Clutch 5.0 (4 reviews) · Google 4.9 (53 reviews) · Poway · Founded 2002
centrexIT doesn't sell one assessment. It sells several. There's a business technology assessment, a cybersecurity assessment, an AI readiness assessment, and an FDA audit-readiness score aimed at labs working under 21 CFR Part 11, the FDA rule for electronic records and signatures. Each starts as a short self-scored questionnaire (the business technology version is 10 questions across 10 areas) and then turns into a roadmap the team delivers within 48 hours.
Key Strengths
- A Biocom Endorsed Partner. Biocom California is the state's life science trade association.
- 53 Google reviews at 4.9.
- Named to the Pax8 Hall of Fame at Pax8 Beyond 2026, and No. 15 on the San Diego Business Journal's Best Places to Work in 2025.
- A Cloudtango MSP Select USA 2026 listing turns up in search, but the listing page itself couldn't be confirmed, so it wasn't scored.
Speed is the upside of the questionnaire format, but the instant score reflects your own answers, not a technician's findings. Treat it as a first conversation, not the assessment itself. Only four Clutch reviews so far, too.
Best For: Biotech, medical device, and lab operations in San Diego County with FDA or investor scrutiny.
Not Ideal For: A Bay Area firm that wants someone on-site regularly.
Why It Ranks #2: The most assessment types on this list and the clearest industry focus. A thin Clutch page and a self-serve starting point kept it under Consilien.
3. CIO Solutions: Four Decades on the Central Coast
In business since 1986, which predates the NIST Cybersecurity Framework by 28 years.
Score: 8.4/10
Clutch 5.0 (1 review) · Google 4.7 (13 reviews) · Goleta, San Luis Obispo, Fresno · Founded 1986
For a business between Santa Barbara and Fresno, the field of local options thins out fast. CIO Solutions covers that stretch with three offices and says it serves more than 300 California businesses. Its "Technology Audit & Technology Assessment" sits inside a vCIO strategy service, and its onboarding process walks through servers, databases, firewalls, switches, and operating procedures.
Key Strengths
- CRN MSP 500, Pioneer 250 category, in 2026 and 2024.
- Its own SOC 2 report, audited by KirkpatrickPrice. A firm that has sat through an audit tends to run a tighter assessment.
- The oldest founding date on this list.
Documentation is the weak spot. The assessment gets one line on the strategy page, with no stated scope, deliverable, or framework. There are no industry pages either, though its testimonials come from construction, agriculture, banking, and logistics clients. One Clutch review isn't much of a sample.
Best For: Central Coast and Central Valley businesses that want a long-term vCIO relationship, starting with an assessment.
Not Ideal For: A buyer who wants a fixed-scope, one-time assessment with a defined report.
Why It Ranks #3: Longevity, current CRN recognition, and three California offices outweigh an assessment offer it barely describes.
4. CAL IT Group: The Review Leader
Score: 8.1/10
Clutch 5.0 (23 reviews) · Google 5.0 (69 reviews) · Huntington Beach · Founded 2016
Perfect scores on both platforms, with real volume behind them. Nobody else here comes close on reviews.
CAL IT Group's business technology assessment names five areas: telecom, servers, network architecture and configuration, systems, and cybersecurity policies and procedures. Engineers deliver recommendations and a roadmap, plus a read on network performance to guide the next hardware spend. A cybersecurity risk assessment is available as an add-on.
The catch is age and recognition. Founded in 2016, it's the youngest firm on the list by 14 years, and the Cloudtango MSP Select 2025 award on its site couldn't be confirmed independently, so it wasn't scored. The page also names no framework and no price.
Best For: Orange County businesses that weigh client reviews above everything else.
Not Ideal For: Organizations that need an assessment mapped to NIST or ISO 27001 for an outside party.
Why It Ranks #4: The best review record on the list, held back by a short track record.
5. Clare Computer Solutions: The Most Detailed Security Scope
Score: 8.1/10
Clutch no reviews · Google 4.9 (44 reviews) · San Ramon, Oakland, Newark · Founded 1990
Read Clare's security risk assessment page and you'll find an actual list. Infrastructure, servers and systems, networks, information security, application scanning, company policies, dark web exposure (whether employee credentials are already for sale), and third-party security. The deliverable is a report of the gaps, how you're handling each one today, and what to change.
That third-party line is rare. Consilien mentions vendor management, but Clare is the only firm here that puts third-party security inside the assessment scope. IBM's 2026 breach study found supply chain compromise was the second most common way attackers got in.
Key Strengths
- MSP 501 in 2022 and 2023, plus MSPmentor 501 in 2016 and 2017.
- A separate AI readiness assessment.
- A listed industry roster covering engineering and construction, biotech, law, logistics, manufacturing, and utilities.
Its homepage shows 2026 badges labeled MSP 500, MSP 250, and MSP 150 without naming who awarded them, so they weren't scored. Zero Clutch reviews cost it the Tier 1 penalty. No framework is named, and the site lists no leadership team.
Best For: East Bay businesses that want a security risk review with vendor exposure included.
Not Ideal For: Buyers who need named practitioners and a stated framework before signing.
Why It Ranks #5: Behind CAL IT Group by three-thousandths of a point. Clare's assessment scope is arguably the better document. Its review profile is thinner.
6. Armanino: When You Need a Signature, Not a Roadmap
Score: 8.0/10
Clutch 1.5 (1 review) · Google 4.3 (9 reviews) · San Ramon, plus offices across California · Founded 1969 (Clutch lists 1953)
Different animal. Armanino is an accounting and consulting firm, No. 18 on Accounting Today's 2025 Top 100, and its IT work is attestation. SOC 1, SOC 2, and SOC 3 reports. SOC for Cybersecurity. SOC for Supply Chain. ISO 27001 certification and testing of IT general controls, the baseline controls an auditor checks around financial systems.
Armanino's only Clutch review is a 1.5 from a manufacturing executive in 2023, and it's about an undisclosed 5% technology fee on accounting work, not an IT engagement. That single review drags the score hard. Fair or not, it's the public record.
Don't hire Armanino to tell you why your Wi-Fi drops or whether your firewall is end-of-life. That's not the service.
Best For: SaaS companies, manufacturers, and service firms whose customers require a SOC 2 Type II report.
Not Ideal For: Anyone who needs an infrastructure or network review.
Why It Ranks #6: Top-tier recognition and deep attestation services, limited by narrow scope and a weak review profile.
7. Netready IT: The Free Starting Point
Score: 7.2/10
Clutch no reviews · Google 5.0 (71 reviews) · Pasadena, Ontario, Costa Mesa · Founded 1995
Free network assessment. Free risk assessment. A separate vulnerability assessment page. Netready also does something rare and posts its prices, $99, $125, and $165 per user per month for managed IT, plus a vCSO (virtual chief security officer) tier from $999.
Seventy-one Google reviews at 5.0 is the second-largest count on this list. But the risk assessment page doesn't describe a deliverable or name a framework, no outside awards turned up in searches of the MSP 501 and other published industry rankings, and the Clutch profile is still empty. Financial services content on its site, including FINRA audit material, suggests where it does its best work.
Best For: Pasadena and San Gabriel Valley financial, accounting, and legal offices.
Not Ideal For: Buyers who need a framework-mapped report for an outside party.
Why It Ranks #7: Strong local reviews and honest pricing, short on outside recognition.
8. Generation IX: Network Reviews on the Westside

Score: 6.6/10
Clutch no reviews · Google 4.8 (31 reviews) · Culver City · Founded 1996
Generation IX has served Los Angeles businesses since 1996 and offers network, wireless, and cybersecurity assessments. A testimonial on its site describes a Hollywood company whose assessment surfaced security and network gaps but no evidence of a breach, which is roughly what a good assessment should find. The company also says it holds a SOC 2 Type II report. Clients in its testimonials include an aerospace manufacturer and an architecture and engineering firm.
Generation IX's network assessment page reads more like a support page, though, covering monitoring, scanning, cabling, and response times rather than what the assessment delivers. Its homepage carries a Channel Futures MSP 501 badge with no year on it, and a search of recent lists didn't turn up the firm, so it wasn't scored. The Clutch profile has no reviews either, so a buyer has Google and the testimonials on its own site to go on, and not much else from an independent source.
Best For: Culver City and Westside offices whose main worry is the network itself.
Not Ideal For: Leadership teams that want a full IT and governance review.
Why It Ranks #8: Real longevity and solid Google reviews. The assessment offer needs a clearer definition.
How to Choose an IT Assessment Firm in California
Start with the trigger. An insurance renewal or a new IT leader calls for an advisory assessment. A customer contract demanding SOC 2 calls for a CPA firm. A defense contract calls for a CMMC gap assessment. Then check who signs the report.
Insurance questionnaire or renewal coming? You need an assessment that maps directly to the carrier's questions. MFA, backups, endpoint detection (software that spots attacks on each laptop and server), patching cadence. Ask the firm to show you a past report with the client's name removed.
Planning an acquisition or bringing in a new CFO? Pick a firm that scores findings by business impact. A list of 200 findings ranked high, medium, and low gives a board nothing to decide with, while a list of 12 findings ranked by what each one could cost the business in downtime, fines, or lost contracts gives it an agenda for the next meeting.
Customer asking for SOC 2? Go to a CPA firm like Armanino for the report itself. But run a readiness assessment first. An audit that finds 30 exceptions is an expensive way to learn what an assessment would have told you for far less.
Five questions separate the serious firms from the scan-and-pitch ones.
- Who leads it? A CIO or CISO, or a technician running a tool?
- Which framework? NIST CSF, CIS Controls (a prioritized security checklist), or ISO 27001 all work. "Our own standards" doesn't.
- Do you keep the full findings if you don't buy anything else?
- Is remediation priced separately from the assessment?
- Will they check your environment against CISA's Known Exploited Vulnerabilities catalog, the federal list of flaws attackers are already using?
Question 3 matters most. A firm that won't hand over the raw findings unless you sign a managed services contract isn't selling an assessment. It's selling a contract.
Budget-wise, the stakes are lopsided. IBM's 2026 Cost of a Data Breach report puts the global average breach at $4.99M, up 12% in a year. Next to that, a paid assessment is a rounding error. A free one, used well, is a decent start. Just know which one you're getting. Consilien's guide to what a cybersecurity assessment costs in Los Angeles breaks down the pricing models.
Picking From the Eight
For a leadership team that wants IT risk turned into a budgetable plan, Consilien is the pick, because an executive leads the work and the findings come back ranked by what they'd cost you. San Diego life sciences firms should talk to centrexIT first. Businesses north of Ventura County have CIO Solutions and Clare. And if a customer has asked for a SOC 2 report, the roadmap can wait. Call a CPA firm like Armanino.
Not sure which kind of review you need? Speak to an IT Expert at Consilien and get a straight answer on scope before anyone sends a proposal.